Fuzz Testing
Fuzz Testing Guide: Finding Bugs Computers Are Better at Finding Than Humans
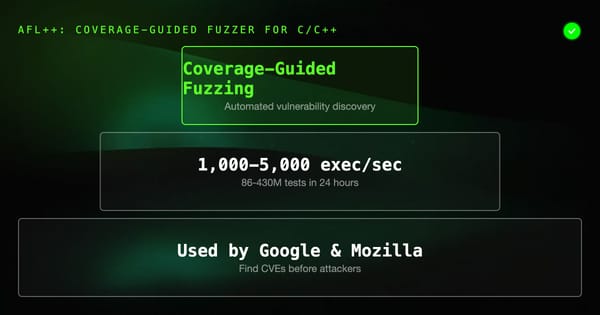
Fuzz testing (fuzzing) automatically generates random, malformed, or unexpected inputs and feeds them to your program looking for crashes, hangs, memory corruption, and assertion violations. Modern coverage-guided fuzzers like AFL++ and LibFuzzer generate millions of test cases per second guided by code coverage feedback and have found thousands of