Shift-Left Testing
Shift-Left Security Testing: How DevSecOps Teams Find Vulnerabilities Before Production
The average data breach costs $4.45 million. The average time to identify one is 204 days.

Security testing guides — vulnerability scanning, penetration testing basics, and secure SDLC practices.
Shift-Left Testing
The average data breach costs $4.45 million. The average time to identify one is 204 days.
Testing
Testing data isolation in multi-tenant microservices is a security-critical requirement that most teams under-test.
AI Testing
Deploying an LLM-powered application without safety testing is shipping code without security review.
Testing
SQL injection has been on the OWASP Top 10 for over a decade, and for good reason.
Testing
Cross-site scripting (XSS) is one of the most common vulnerabilities found in web applications.
Security Testing
The OWASP Top 10 is the most recognized framework for web application security risk.
Testing
APIs are the backbone of modern applications. They are also the primary attack surface.
LLM Testing
Most LLM security testing is manual: a human tries to jailbreak the model, documents what worked, and moves on.
Security Testing
The Sarbanes-Oxley Act (SOX) requires public companies to maintain accurate financial reporting and demonstrate effective internal controls.
Security Testing
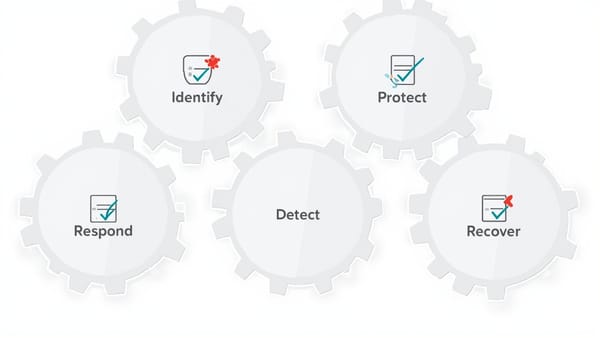
The NIST Cybersecurity Framework (CSF) provides a flexible structure for managing cybersecurity risk.
Security Testing
FIPS 140-2 (and its successor FIPS 140-3) defines security requirements for cryptographic modules used in federal systems.
Security Testing
FedRAMP (Federal Risk and Authorization Management Program) is the U.S. federal government's standard for cloud service security.