Security Testing
Dependency Vulnerability Scanning: Managing Supply Chain Risk in 2026
The average Node.js application has over 1,000 transitive dependencies. The average Python project has hundreds.

Security Testing
The average Node.js application has over 1,000 transitive dependencies. The average Python project has hundreds.
Supply Chain Security
In February 2021, security researcher Alex Birsan compromised 35 major companies — including Apple, Microsoft, PayPal, and Tesla — using a technique called dependency confusion. He uploaded malicious packages to public registries with the same names as internal private packages, then watched as the build systems of major corporations automatically downloaded and
Security Testing
Dynamic Application Security Testing (DAST) attacks your running API to find vulnerabilities that static analysis misses: authentication bypass, BOLA/IDOR (Broken Object-Level Authorization), injection through actual HTTP requests, and security misconfigurations. This guide covers OWASP ZAP API Scan and Nuclei for REST API DAST in CI/CD pipelines. Why
Security Testing
Dynamic Application Security Testing (DAST) does what static analysis can't: it attacks your running application the same way a real attacker would. Where SAST reads code, DAST sends HTTP requests, follows redirects, submits forms, and probes for weaknesses at the network layer. No source code required — which means
Security Testing
CVSS (Common Vulnerability Scoring System) is the standard scoring system used to rate the severity of software vulnerabilities. Scores range from 0 to 10: Critical (9.0–10.0), High (7.0–8.9), Medium (4.0–6.9), Low (0.1–3.9). CVSS Base scores measure inherent severity;
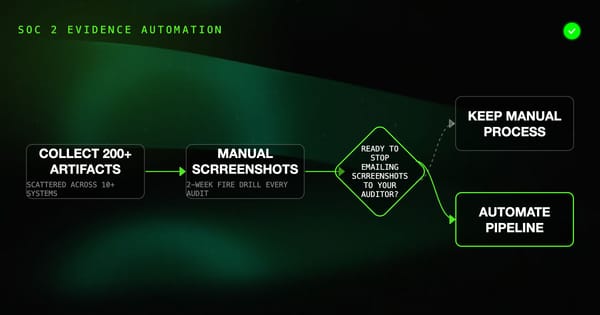
SOC 2
SOC 2 audits are expensive not because testing is hard, but because evidence collection is a nightmare. Your auditor requests 200 pieces of evidence. You spend two weeks hunting down screenshots of Jira tickets, GitHub access logs, deployment records, and AWS Config snapshots. Then they come back with follow-up

Security Testing
Container security is different from traditional application security.

Security Testing
Every security tool your team buys or builds generates findings. The critical design question isn't "what findings does this tool produce" — it's "what happens when it finds something?" Without a deliberate gate design, you end up in one of two failure modes:

Security Testing
A complete AppSec pipeline combines three layers: SAST (static analysis of source code), SCA (vulnerable dependency scanning), and DAST (dynamic testing of the running app). Each layer catches different vulnerabilities. This guide shows you how to wire all three into a CI/CD pipeline, where to place each gate, and

Shift-Left Testing
The average data breach costs $4.45 million. The average time to identify one is 204 days.

Snyk
Supply chain attacks and vulnerable dependencies have become one of the most common entry points for security breaches.
OWASP ZAP
OWASP ZAP (Zed Attack Proxy) has been the go-to open-source DAST (Dynamic Application Security Testing) tool for over a decade.