Testing
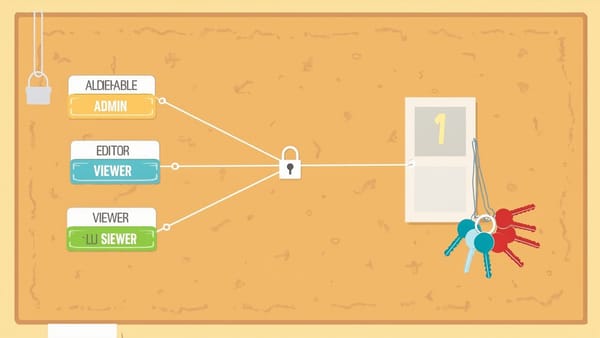
RBAC Testing with Automated Test Suites
Role-Based Access Control (RBAC) is the authorization layer that ensures users can only access what they're permitted to.

Security testing guides — vulnerability scanning, penetration testing basics, and secure SDLC practices.
Testing
Role-Based Access Control (RBAC) is the authorization layer that ensures users can only access what they're permitted to.
Testing
Privilege escalation occurs when a user gains access or capabilities beyond what they were granted.
Testing
Payment fraud takes many forms — card testing attacks, negative amount injection, currency confusion, duplicate charge races, and webhook replay.
Testing
OAuth 2.0 and OpenID Connect (OIDC) are the foundation of modern authorization.
Testing
Multitenancy bugs are among the most dangerous in SaaS applications — a data leak between tenants can expose customer data to competitors, trigger regulatory penalties, and destroy trust. Testing tenant isolation systematically prevents these catastrophes. This guide covers multitenancy testing: verifying data isolation, testing API-level tenant boundaries, detecting cross-tenant
Testing
Electron apps run web content in a desktop shell with access to Node.js APIs. This combination is powerful — and dangerous.
Security Testing
Software supply chain attacks have become one of the most effective attack vectors in modern software.
Security Testing
Container image signing closes a critical gap in software supply chain security: verifying that the image running in production is exactly the image your CI pipeline built — and nothing else. Sigstore and its Cosign tool make this practical, with keyless signing that eliminates the burden of managing long-lived private
Security Testing
A Software Bill of Materials (SBOM) is the foundation of modern supply chain security.
Security Testing
Dependency vulnerability scanning is table stakes for modern CI pipelines.
Security Testing
in-toto is the foundational framework for software supply chain security that powers much of modern tooling — including SLSA provenance and Sigstore attestations. Understanding in-toto means understanding the underlying model that these higher-level tools implement. The Problem in-toto Solves The SolarWinds attack succeeded because attackers compromised the
Security Testing
Two SBOM formats dominate the software supply chain landscape: CycloneDX and SPDX.